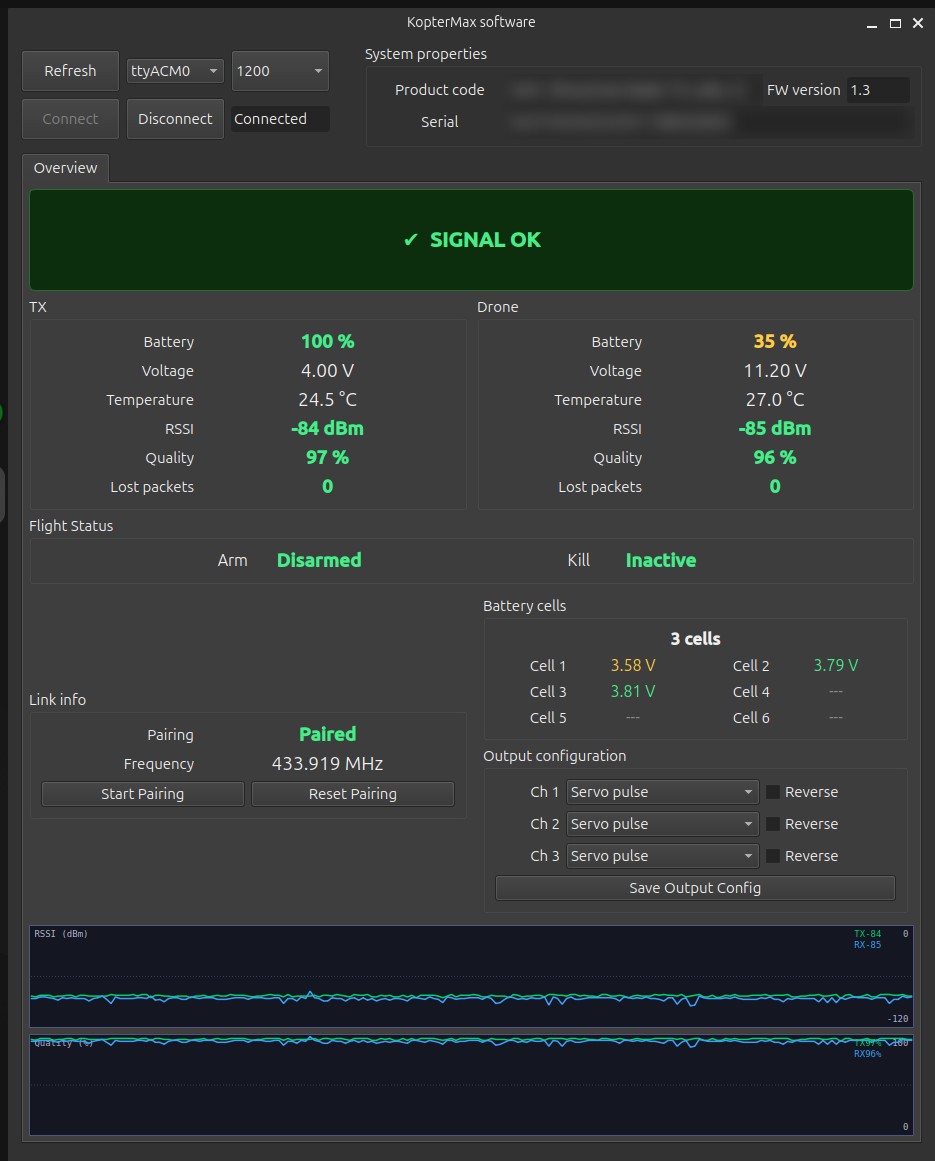
Shutoff and bleed control for rocketry, designed to remain commandable precisely when the primary avionics are the thing that has gone wrong.
Sector: Propulsion test and launch
The constraint
A safety system that shares components, power or software with the system it protects is not a safety system. The requirement was an abort path that stays available when the primary avionics have failed, including when they have failed in an unhelpful way — still powered, still transmitting, no longer correct.
The propellant path additionally has to be made safe on a schedule that does not depend on anything else continuing to work.
What we did
Independence was the first design rule and it was applied throughout: separate power, separate command path, separate processing, no shared failure mode with the primary system.
The system fails in a known direction. Loss of command, loss of power or loss of confidence all resolve to the safe state rather than to an indeterminate one. Arming logic and interlocks were specified so that reaching a commandable-abort state is deliberate and observable, and so the system cannot be armed by accident or left armed by oversight.
Testing was weighted accordingly: the abort path was exercised far more than the nominal path, including under induced failures of the primary avionics, because the abort path is the only one whose reliability is unconditional.